Skip to content
Donovan Cybersecurity
  • Home
  • About
  • Services
    • 01Virtual CISO
    • 02Security Maturity Snapshot
    • 03Risk Assessment & Planning
    • 04Policy & Compliance
    • 05AI Governance
    • 06Security Awareness Training
    • 07Technology & Vendor Advisory
  • Insights
  • Contact

Category: Building the Program

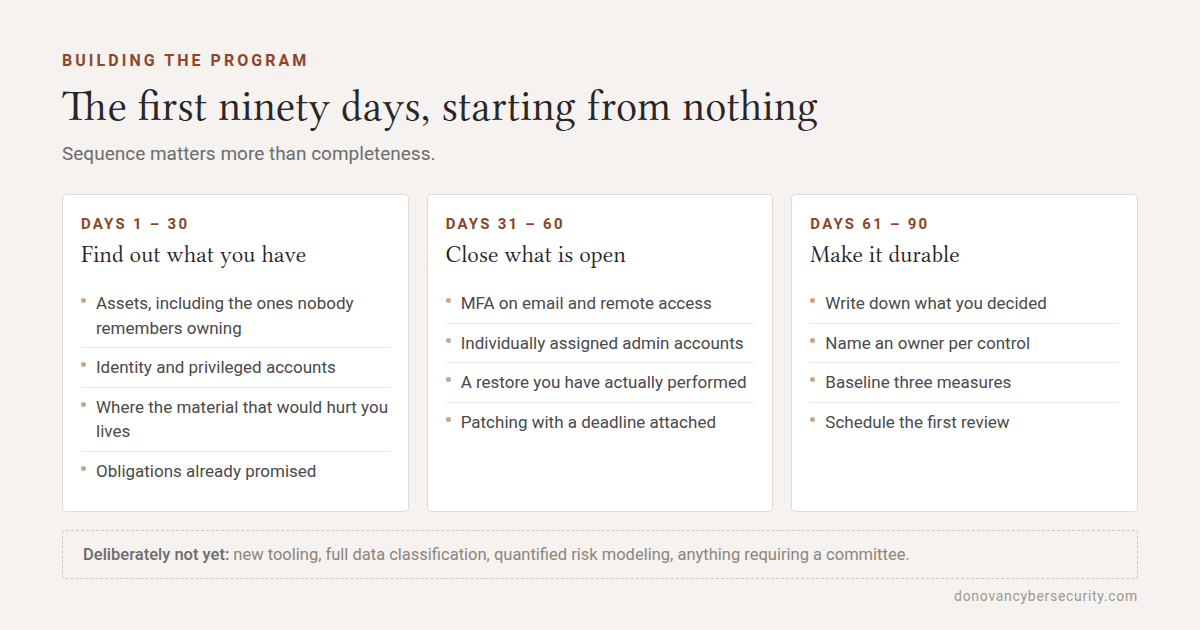
Three-phase diagram of the first ninety days of a security program. Days one to thirty: find out what you have, covering assets, identity, sensitive data and obligations already promised. Days thirty-one to sixty: close what is open, covering multifactor authentication, individually assigned administrator accounts, a restore you have performed and patching with a deadline. Days sixty-one to ninety: make it durable. A footnote lists work deliberately deferred.

The First Ninety Days of a Security Program, Starting From Nothing

October 26, 2026 Donovan Kelley

Sequence matters more than completeness. What to inventory in the first month, which four doors to close in the second, how to make it durable in the third, and what to deliberately leave for next year.

Continue Reading →

Posted in: Building the Program

Recent Posts

  • The First Ninety Days of a Security Program, Starting From Nothing
  • Your People Are Already Using AI. The Only Question Is Whose.
  • Your Cyber Insurance Renewal Is a Security Audit You Did Not Schedule

Recent Comments

    Archives

    • October 2026
    • September 2026

    Follow Me

    • LinkedIn

    Contact Me

    • Email
      donovan.kelley.it@gmail.com
    • Phone
      1-727-417-4735
    • Address
      St Petersburg, FL
    • Home
    • About
    • Services
    • Insights
    • Contact
    Copyright © 2026 Donovan Cybersecurity LLC