
Policies people follow, controls auditors accept
A practical policy set and control alignment that holds up to audits, customer security reviews, and cyber insurance questionnaires.
Most organizations sit at one of two extremes: nothing written down, or a binder of purchased templates nobody has read since. Neither survives an audit or a serious customer security review. I build a policy set sized to your organization, in plain language, mapped to the frameworks your customers and regulators actually ask about, and then help you demonstrate that the controls behind it operate.
What Gets Built
Documentation and evidence that do real work.
01
Policy Set
Acceptable use, access control, data classification, incident response, vendor management, business continuity and the rest, written for your organization rather than lifted from a template.
02
Control Mapping
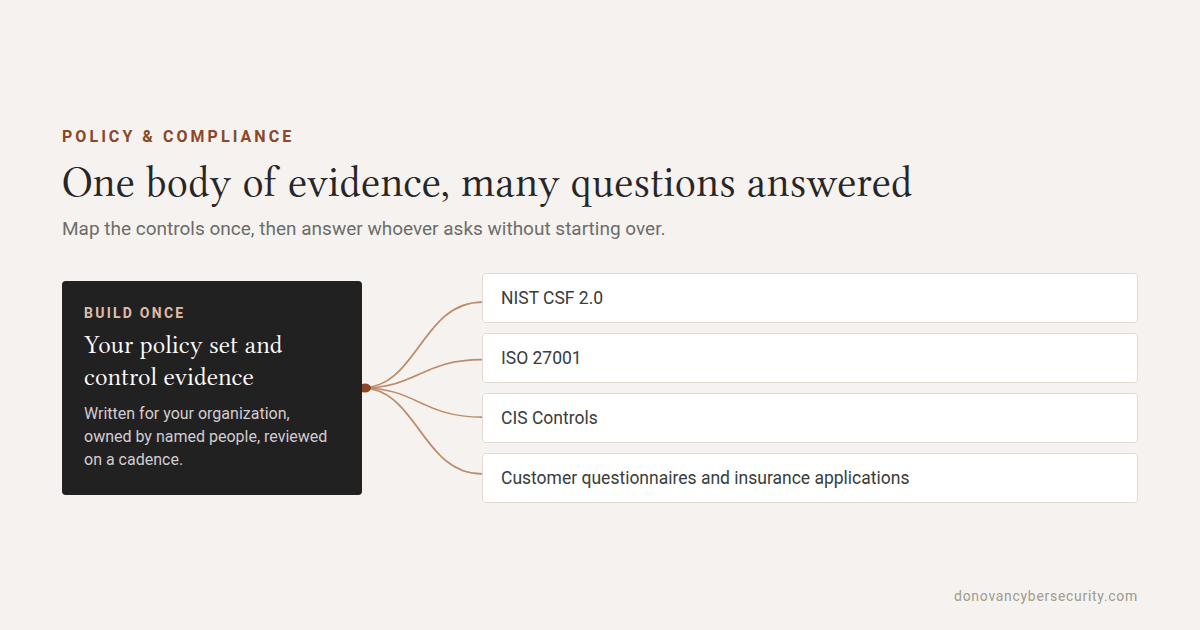
Your controls aligned to NIST CSF 2.0, ISO 27001, or CIS Controls, so a single body of evidence answers many different questions.
03
Evidence & Audit Readiness
The artifacts auditors ask for, including records, approvals, and review cycles, organized before the request arrives rather than after.
04
Questionnaire Response
Consistent, defensible answers to customer security questionnaires and cyber insurance applications, plus a plan for the gaps they expose.
Where Policy Programs Fail
OWNERSHIP
A policy with no owner
A policy with no named owner and no review date is a document, not a control. Every policy gets an owner, a review cadence, and a defined path for exceptions.
PROPORTION
Right-sized to the organization
A two-hundred-page policy set at a hundred-fifty-person company guarantees non-compliance. Scope follows real risk and real capacity to sustain it.
Part of a broader program
Policy work lands best on a clear picture of risk. A Security Maturity Snapshot or a security risk assessment shows which policies matter most, and Virtual CISO engagements keep the set current as the business changes.
Get your policy set in order
A 30-minute conversation is usually enough to size the work and set a sequence.